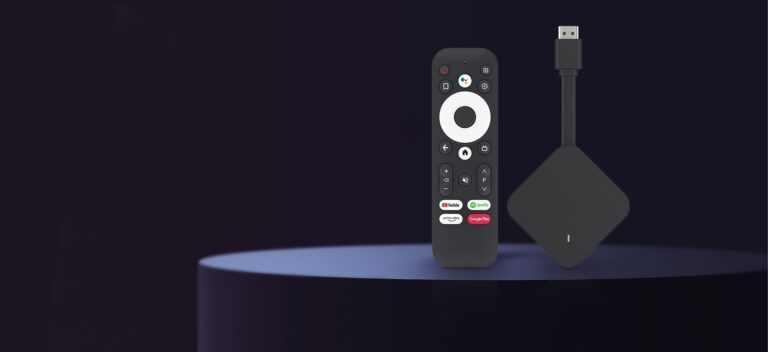
Google confirmed on November 2, 2026, that one of its Android manufacturing partners had secretly installed a backdoor in approximately 1.3 million set-top boxes, enabling the devices to be hijacked and used as part of a botnet. The affected hardware was produced by Videostrong Technology Co., a Shenzhen-based company that supplies Android TV boxes under various white-label brands. According to Google, the backdoor allowed unauthorized remote access, potentially enabling coordinated attacks or data harvesting without users’ knowledge.
The discovery prompted immediate action from Google’s security teams, who worked to identify and neutralize the malicious infrastructure. Google stated it has since dismantled the backdoor’s command-and-control mechanisms, effectively disabling the botnet’s operational capacity. In addition, the company announced it has “cut ties” with Videostrong Technology Co., ending all business relationships and removing the partner from its approved hardware ecosystem.
Videostrong has not publicly responded to the allegations, and Google did not disclose whether legal or regulatory actions are pending. The incident highlights ongoing risks in the global supply chain for consumer electronics, particularly where firmware integrity and vendor oversight are concerned. For content creators relying on Android TV devices for streaming, production monitoring, or audience engagement, the event underscores the importance of verifying device provenance and applying regular firmware updates.
Google advises users to ensure their devices are running the latest software and to factory-reset any suspect units if unusual behavior is observed. While no widespread data breaches have been reported linked to this botnet, the scale of the compromise—affecting over a million devices—makes it one of the largest known incidents involving manufacturer-level firmware manipulation in recent years. The case serves as a stark reminder that trust in hardware partners must be continuously validated, especially in an era where smart devices are integral to both personal and professional workflows.
Join the conversation
Load Facebook comments to read and reply using your Facebook account.